Controlled & ethical
Every action is controlled, ethical and compliant.

AI-ASSISTED SECURITY OPERATIONS
PeLeK AI unifies scope, tool output, finding prioritization and reporting into one safe workflow. Risky steps never run without human approval.
Every action is controlled, ethical and compliant.
Every risky action requires explicit human approval.
Tests run only on approved, in-scope assets.
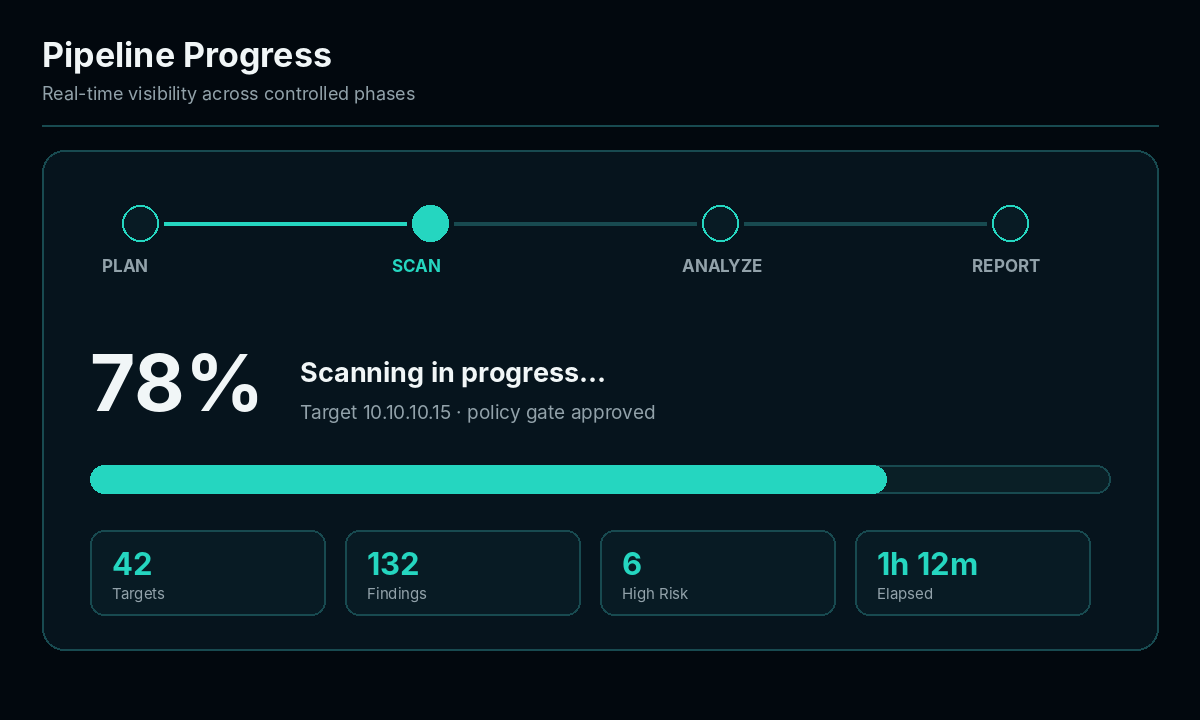
Recon → detection → active validation → report.
Every action is logged and fully auditable.
Define scope, rules and objectives.
AI-assisted scanning within boundaries.
Findings correlation and risk analysis.
Structured report and audit log.
 Built with security by design. You stay in control.
PeLeK AI is an AI-assisted penetration testing platform built for security teams. It orchestrates tools and data under strict policies, keeping humans in control the entire time.
 4Phase PipelineRecon to Report100%Human ApprovedRisky Actions
 FullAuditabilityEvery Action
 EnterpriseReadySecure by Design

All actions follow defined rules and require explicit approval for risk.

Recon, detection, active validation and reporting in one structured flow.

Correlates signals, reduces noise and focuses on real risk.

Runs only on allowed targets with authenticated context.

Secure outbound tunnel for controlled remote environments.

Clear, executive-ready reports and audit evidence.
 PlanScanAnalyze
 Report
Run scans from the platform within approved boundaries.
Remote AgentTLS / WSS 443 Command Center
 Isolated Namespace
 Authorized Target
Agent establishes outbound tunnel. All actions remain policy-controlled.
Every risky command requires explicit human approval.

Targets and inputs are allowlisted and sanitized before execution.
No DoS, brute-force or data-destructive operations.
Operations stay in isolated namespaces via localhost.
Full audit log with tamper-evident records.
Signed agent, auto updates and short-lived tokens.
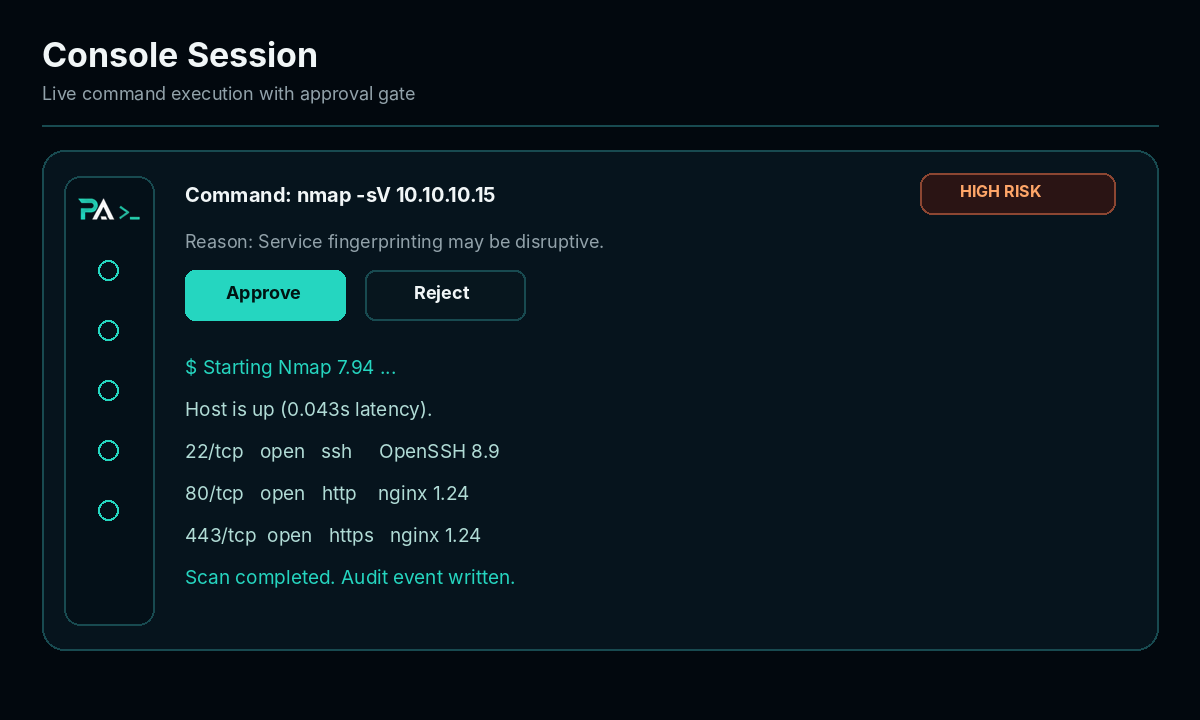
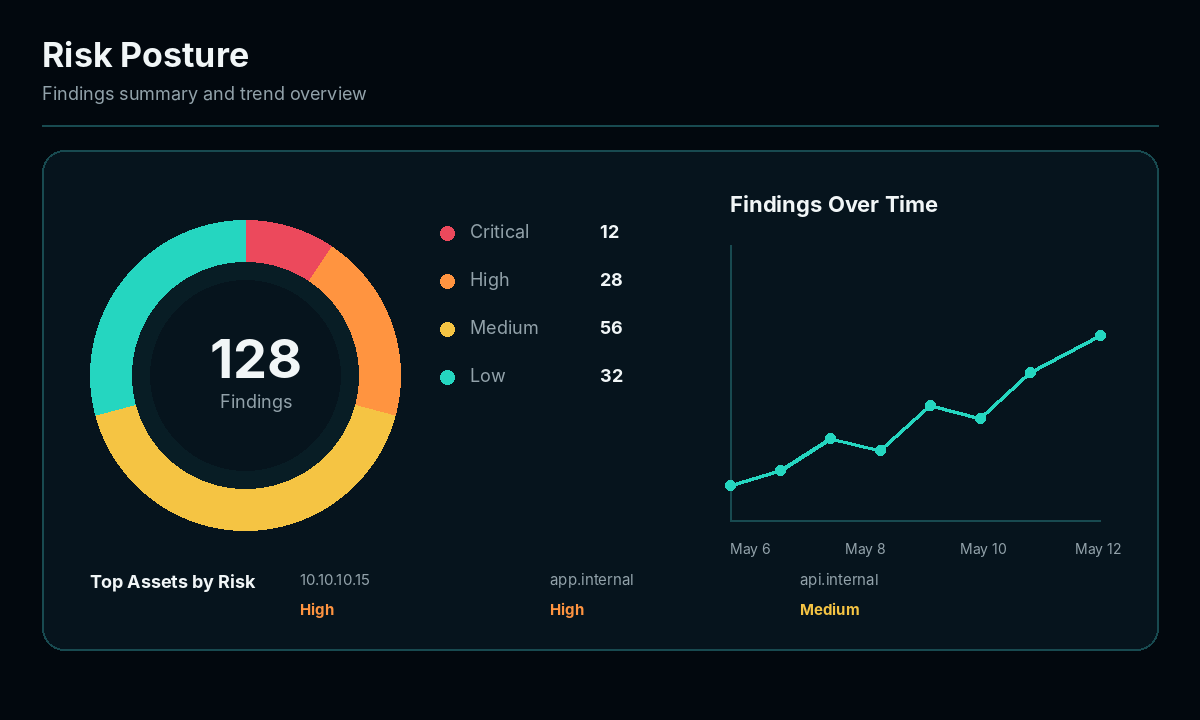
See PeLeK AI in action with a guided Proof of Concept. We validate within your environment and policies.
Tell us about your use case and environment.
We define scope, policies and access.
Hands-on evaluation with our expert team.
Receive findings report and roadmap.
PeLeK AI Remote Agent enables secure, outbound-only access to internal or remote networks without opening inbound ports.
Remote AgentTLS / WSS 443Command CenterIsolated NamespaceAuthorized TargetFor PoC requests, technical questions or project inquiries.